
 Partner Login
 Customer Support

 Fibre Termination
 Wi-Fi Routers
 Wi-Fi Access Points
 Value-added Services
Sága Wi-Fi 7 Routers
Designed for peak performance and easy refurbishment.
Find out more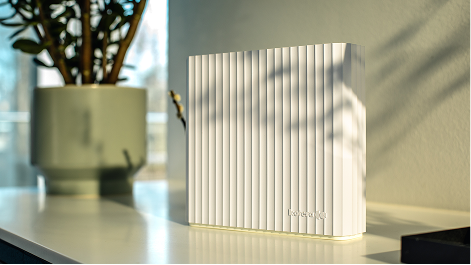
Icotera Vulnerability Disclosure Policy
At Icotera we are committed to providing CPE products that allow its customers to easily and effectively protect their users and their network from malicious actions.
This is done by ensuring the security of our Consumer Premises Equipment (CPE) products software and configuration recommendations.
This Vulnerability Disclosure Policy outlines the procedures for security researchers and individuals to responsibly report potential vulnerabilities in our products.
Issues relating to product security are handled by the Icotera Product Security Incident Response Team (PSIRT).
– Product vulnerabilities and security incidents – psirt@icotera.com – Use this address for any suspected vulnerability or security weakness in an Icotera CPE product, its firmware or an associated service, and for any security incident affecting an Icotera product in operation. It is Icotera’s single point of contact for these reports and is monitored by the PSIRT.
– All other security matters – security@icotera.com – Use this address for security questions and concerns that do not relate to an Icotera product — for example, our website, our corporate IT, or e-mails and domains impersonating Icotera.
– If you are not sure which applies, write to psirt@icotera.com. We would far rather receive a report at the wrong address than not receive it at all, and we route it internally. A report sent to security@icotera.com that turns out to concern one of our products is passed to the PSIRT and handled under this policy.
– Encrypt your email using our PGP key to ensure the confidentiality of the communication.
– Include your contact information, including your name and email address.
– Icotera is committed to acknowledging receipt of your report within 72 hours.
– We will provide regular updates on the status of the investigation.
– Registering a report is not in itself a confirmation that a vulnerability exists.
– Security researchers are expected to make reasonable efforts to avoid privacy violations, service disruptions, and destruction of data during their research.
– Do not disclose the vulnerability to the public or any third parties until Icotera has had a reasonable time to address the issue.
– Icotera is committed to working with security researchers to understand and address reported vulnerabilities promptly.
– We will provide public credit and recognition to the security researcher, with their consent, upon successful resolution of the vulnerability.
– Icotera will not pursue legal action against individuals who discover and report vulnerabilities in accordance with this policy.
– This policy does not grant permission to engage in any activities that could harm Icotera or its customers.
– Icotera reserves the right to update this policy at any time without notice.
– For any questions or concerns regarding this policy, please contact security@Icotera.com.
– Icotera PGP key can be found here.
Thank you for helping us keep our products secure!
Icotera Security Team
| Product | Product Security Update Period & End of Support |
|---|---|
| Baldur f2140 Baldur f2141 Baldur f2240 Baldur f2241 | 5 years (until 31 December 2031) |
| Baldur fX310 Baldur fX311 Baldur fX410 Baldur fX411 Baldur fX710 Baldur fX711 | 5 years (until 31 December 2031) |
| Sága r2501 Sága r2701 | 5 years (until 31 December 2031) |
| i4860 | 5 years (until 31 December 2031) |
| i6401 i6405 i6407 | 5 years (until 11 December 2027) |
| i3550 i4850 | 5 years (until 1 January 2027) |
| i5204 i5208 | 5 years (until 11 December 2027) |
| i3560 i4862 i4882 i4883 | 5 years (until 11 December 2027) |
| i5901 i5905 i6901-20 i6905-20 | 5 years (until 1 January 2027) |
| i7208 i7404 i7408 | 5 years (until 11 December 2027) |
| Note: Products not listed here are either “End of Support” or in the “New Product Introduction” phase. | |